The quickest way to build a strong supplier vetting process is to turn business needs into clear, weighted checks, verify legal and financial standing, and lock your decisions to evidence. This ultimate guide to the supplier vetting checklist uk shows exactly what to ask, how to score risk, which documents to keep, and how to run fair, sealed competitions.
What Is a Supplier Vetting Checklist and Why It Matters
A supplier vetting checklist is a structured set of questions, documents and decision points that lets you judge if a vendor is safe, compliant and capable before you award work. For UK organisations, it anchors procurement in repeatable governance: you check what is relevant, record why you decided, and keep an audit trail you can stand behind in 2026 and beyond.
Without structure, vetting drifts into email threads and gut feel. That increases the chance of missing a liability (for example, uninsured subcontractors) or overlooking a performance red flag (such as weak references on a critical service). A clear framework turns due diligence into steps that anyone on your team can run, even under time pressure.
Use a checklist to define what “good” looks like, calibrate scores across reviewers, and evidence every judgement. Build it once, iterate as risks change, and use it across tenders. When you need to move quickly, the supplier vetting checklist uk helps you move safely.
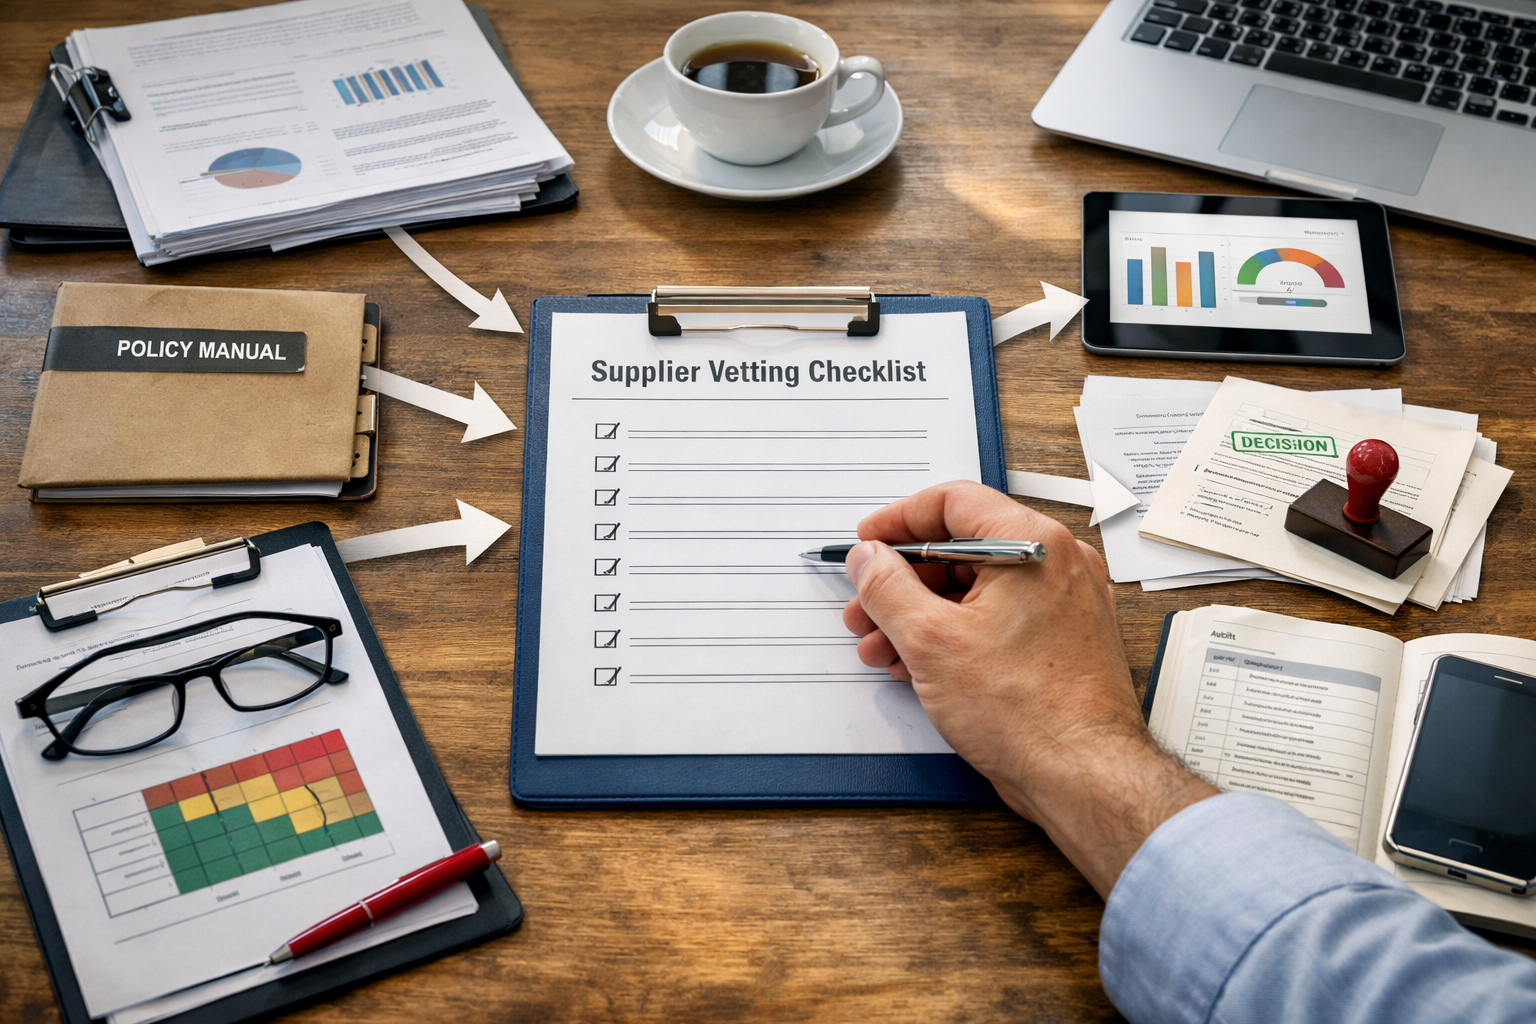
Imagine a 40-person firm buying managed IT support. With no checklist, you might rely on a glossy proposal and a single reference. With a robust approach, you test response times, review data handling, confirm financial resilience and align SLAs to business impact. The end result is not just a better supplier—it’s a better night’s sleep for your leadership team.
The Practical supplier vetting checklist uk (2026 Edition)
Use this practical sequence to build or refine your vetting flow. It maps neatly to both informal buys and full tenders, whether you are a start-up or an enterprise group consolidating categories.
- 1) Translate your brief into testable requirements. Turn plain-English goals into measurable criteria (e.g., “Resolve P1 incidents in 30 minutes”). Group them as must-haves, should-haves and value-adds. Avoid vague wording; test with a colleague for multiple interpretations.
- 2) Weight criteria transparently. Assign percentages by impact: capability, cost, risk and service quality. Cap any single factor to prevent over-weighting (e.g., keep price below 40% unless regulated otherwise). Publish weights to participants.
- 3) Screen for eligibility. Confirm registration, VAT, insurance, certifications (ISO/IEC 27001 for information security, ISO 9001 for quality), and whether they can accept your standard terms for the spend level. Record any exceptions.
- 4) Identity and status checks. Use Companies House to verify directors, filings and status. Confirm ultimate beneficial ownership and any name changes. Note any active charges or proposals to strike off.
- 5) Financial health and credit risk. Review recent accounts, liquidity and gearing. For smaller suppliers, evaluate sustainability of cash flow, not just credit scores. Decide thresholds by contract criticality.
- 6) Safety, environment and ethics. Validate H&S policy, incident reporting, environmental commitments, and modern slavery statements where applicable. Ask for evidence, not promises.
- 7) Data protection and confidentiality. Confirm UK GDPR compliance, technical/organisational measures, data processing roles, and breach history. For high-risk processing, ask for DPIA outcomes or summaries.
- 8) Technical fit and service design. Map how the supplier will deliver. Request architecture diagrams, SLAs, RTO/RPO targets (for services), and sample reports. Check capacity planning, onboarding and exit plans.
- 9) References and case alignment. Seek two to three relevant references. Ask about delivery variance, issue resolution and partnership behaviours. Score on relevance over brand names.
- 10) Pricing clarity and total cost. Itemise unit rates, assumptions, indexation and change costs. Compare apples-to-apples using a pricing template. Test scenarios (peak usage, change requests).
- 11) Security of bids and fairness. Keep pricing and responses sealed until the deadline. Pre-define Q&A windows and share clarifications with all bidders to ensure parity.
- 12) Evidence-locked evaluation. Score requirement-by-requirement with commentary and links to passages in the bid. Require reviewers to justify non-compliance calls and highlight trade-offs.
- 13) Moderation and approval. Run a moderation session to resolve scoring deltas. Keep the final award decision with named approvers and a documented rationale.
- 14) Onboarding conditions. If selected, confirm certificates, insurances and data processing agreements before go-live. Create a “first-90-days” plan.
For a deeper write-up on shaping your requirements into a strong tender, see the Beginner‑to‑Expert checklist for writing tenders.
What Laws, Standards and Policies Should You Check Against?
Your checklist should reference the laws and policies that shape due diligence. Even if you are not a contracting authority, building to public‑sector discipline protects you in audits and reduces downstream issues.
- Procurement policies and PPNs. If you work with public bodies or mirror their standards, monitor the UK government’s Procurement Policy Notes collection for updates on transparency, carbon reporting, or prompt payment expectations.
- Company identity and status. Validate company details on Companies House: Get information about a company. Match registered names to bid entities and check filing behaviour and insolvency notices. Note any persons with significant control.
- Data protection (UK GDPR). If personal data is involved, align with the ICO’s UK GDPR guidance. Confirm roles (controller/processor), cross-border transfers, retention, incident response, and subcontractor use.
- Health & Safety and environment. Expect clear policies, training records and incident logs. For higher-risk works, require method statements and risk assessments. Seek ISO certifications where they add assurance, but focus on substance over logos.
- Ethical sourcing and modern slavery. For relevant spend and turnover thresholds, request accessible policies and statements. Even when not mandated, set expectations for supply chain transparency and escalation routes.
Translate these references into yes/no gates and scored criteria. For example, “UK GDPR-compliant with DPIA available” could be a 10-point criterion with a pass mark of 7 and a non-negotiable data breach clause. Build your process once and refresh quarterly, so your supplier vetting checklist uk remains current without rework.
Keep an eye on internal policies too: information security baselines, ESG commitments, and payment terms. Align your vetting so suppliers know exactly what “good” entails. That transparency prevents misbids and accelerates onboarding post-award.
How Do You Score Risk Versus Value Without Bias?
Great vetting reduces subjectivity. The challenge is balancing innovation and value with the duty to protect your organisation. A well‑designed scorecard creates a fair comparison where strong offers rise to the top for the right reasons.
- Start with business impact. Map what failure would cost: service outage, regulatory exposure, safety incidents, or reputational harm. Heavier impacts deserve higher weights on control measures and resilience.
- Use weighted criteria and anchor descriptions. For each criterion, define what a 10, 7, 5 and 0 looks like. This “anchoring” keeps reviewers consistent across suppliers and time.
- Separate compliance gates from scored value. Mandatory checks (e.g., minimum cyber controls) are pass/fail. Value elements (e.g., proactive optimisation) are scored. Don’t let a glossy value-add mask a failed gate.
- Blind scoring where possible. Remove brand cues, award history and pricing until technical scoring is complete. This mitigates halo effects and familiarity bias.
- Moderate to consensus. After individual scoring, run a moderated session to resolve deltas. Record reasons for adjustments and keep the final decision with named approvers.
- Red Team for ambiguity. Invite a reviewer who did not draft the requirements to challenge unclear wording and exploitable gaps before the tender goes live.
Bias creeps in when criteria are vague, scoring anchors are absent, or bids are reviewed in different levels of detail. Make the process predictable and evidence-led.
Tools can help you make this discipline sustainable. For example, in TenderLock, criteria have defined weights, reviewers score requirement-by-requirement with commentary, and moderation creates a single, auditable record. Calls with shortlisted suppliers can be recorded with AI summaries so you compare like with like without relying on memory.
Manual Spreadsheets vs Procurement Platforms: Which Fits Your Team?
There’s no one-size-fits-all approach. Your choice depends on team size, deal complexity and the need for auditability. Use the table below to compare common options.
| Approach | Setup Time | Data Integrity | Audit Trail | Risk Scoring | Cost at Small Scale | When It Fits |
|---|---|---|---|---|---|---|
| Ad‑hoc emails + spreadsheets | Very fast to start | Prone to version drift and missed cells | Low; decisions buried in emails | Manual formulas; hard to keep consistent | Minimal licence cost | One‑off, low‑risk buys with low scrutiny |
| Standard document templates | Moderate; needs maintenance | Better consistency if well governed | Partial; relies on team discipline | Improved, but still manual moderation | Low | Growing teams formalising process |
| TenderLock procurement platform | Fast; AI builds structure from your brief | Bids sealed; single source of truth | Full trail: evidence‑locked scores, approvals, calls | Weighted criteria with moderation and dashboards | First live tender free | Teams needing repeatable, auditable workflows |
If you are frequently asked to “show your working” to leadership or auditors, platforms pay for themselves in time saved and risk avoided. When your pipeline is occasional and low risk, sharpen your templates and enforce version control—with the understanding that diligence depends on people keeping to the process.
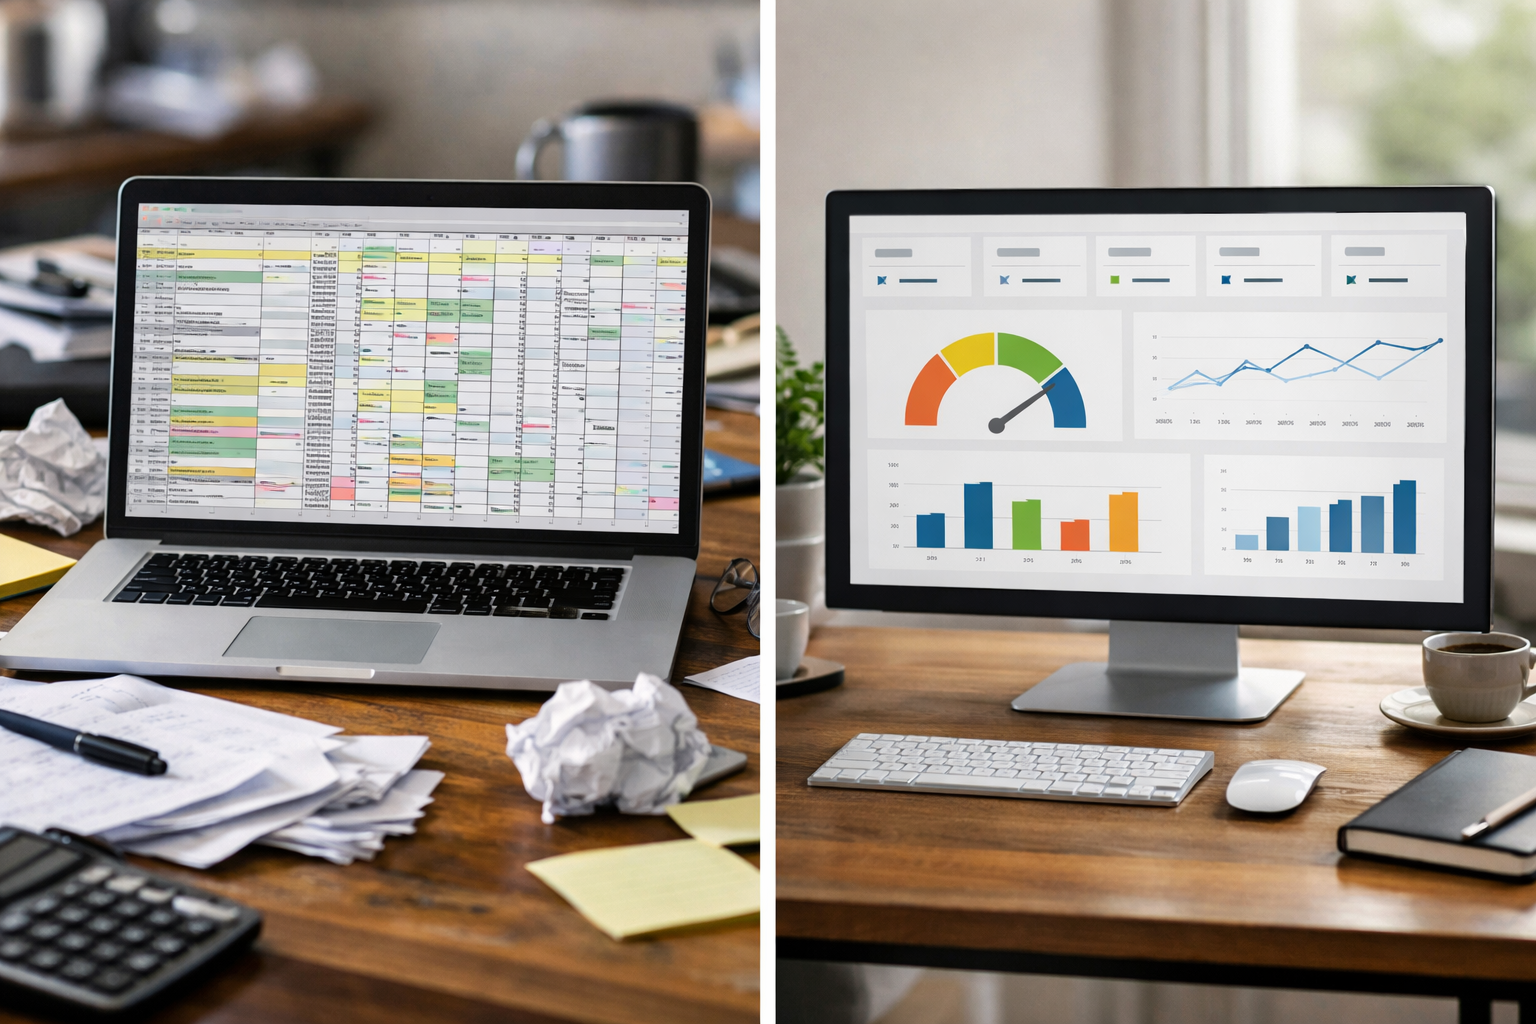
For mixed portfolios, some teams start with a platform on critical categories while they improve templates elsewhere. That staged approach keeps momentum without forcing a single answer across all spend types.
How TenderLock Automates Vetting Without Surrendering Control
TenderLock is built to convert a plain-English brief into structured requirements, sealed bids and evidence‑locked evaluations—while keeping the final decision with named people. It lets you move faster without lowering the bar.
- From brief to criteria. Paste your objectives; AI suggests structured requirements, weights and pass/fail gates. You can add, remove or reweight in minutes, then run a Red Team check for ambiguity.
- Sealed bidding. Supplier responses and prices stay locked until the deadline. Q&A is centralised; clarifications are shared fairly with everyone.
- Requirement‑level checks. Reviewers score each response against the criterion, attach evidence, and flag risks. Moderation creates a single position, with named approvers recording the final award.
- Vetting shortcuts, safely done. Integrated checks pull in Companies House data and Creditsafe scores, so you confirm identity and financial health without tab‑hopping.
- Conversations captured. Recorded calls with AI summaries mean every promise is traceable. No more “he said, she said”—just searchable notes tied to the tender.
- Governance by default. Dashboards show progress, outliers and deadlines. A full audit trail is created automatically.
Mid‑process and want to see it live? Start your first live tender free with no card required. You’ll have a working checklist, sealed competition and audit trail before the week is out.
Whether you use TenderLock or another approach, keep one principle: scoring should be traceable to the question asked and the answer given. That’s how a supplier vetting checklist uk becomes something auditors trust and suppliers respect.
What Evidence Should You Lock, Store and Audit for Governance?
Evidence is your defence if a decision is challenged and your memory when staff move on. It’s also your playbook for continuous improvement: looking back at what correlated with great delivery and what didn’t.
- Approved requirements and weights. Keep the baseline you actually used to score. If you changed weights during moderation, store both versions with the rationale.
- Supplier submissions and Q&A. Archive bids exactly as received, plus every clarification asked and answered. For parity, show that all bidders had access to the same information.
- Scores with commentary. For each criterion, maintain the score, reviewer notes and links to the exact passage in the bid. You should be able to answer “why did we give a 7, not a 9?” six months later.
- Checks and certificates. Save copies of insurances, accreditations and critical policies, with expiry dates and review reminders.
- Recorded interactions. Where permitted, record supplier meetings and store AI summaries. This is invaluable when you need to verify commitments or share insights across teams.
- Approvals and award rationale. The final decision, approvers’ names, conflicts managed, and communications to winners and losers—all time-stamped.
Consider access controls: not everyone needs to see pricing or raw financials. Role‑based permissions reduce accidental disclosure. For retention, follow your policy; many teams keep full tender records for multiple years to cover warranty periods and regulatory needs.
Finally, audit yourself. Run a quarterly review of two to three awards. Did the evidence stack up? Were weights followed? Did post‑award outcomes match expectations? Feed that learning back into your templates and training.
How to Run Sealed, Fair Bidding With Vendor Confidence
Sealed bidding protects integrity and builds supplier trust. When vendors know their prices and proposals are locked until the deadline, they focus on their best offer rather than gaming each other. For buyers, sealed processes deliver comparability and defensibility.
- Set the rules early. Publish timelines, scoring weights and Q&A windows. State how tie‑breaks work, who moderates, and when feedback will be given.
- Centralise clarifications. Route all questions through a single channel and share non‑confidential answers with all participants. Keep a visible log.
- Lock responses. Enforce deadlines sharply. Late submissions risk fairness; only accept them under exceptional, pre‑defined conditions.
- Blind technical scoring first. Hide commercial data until technical scores are finalised. Then open pricing to complete total value calculations.
- Explain the outcome. Give constructive, evidence‑based feedback aligned to published criteria. This grows market capability and supplier goodwill.
For a step‑by‑step view of sealed competitions, read our practical walkthrough of sealed bidding with AI support. When done right, sealed processes dovetail with your supplier vetting checklist uk to make awards fair and repeatable across categories.
Tooling helps, but discipline wins the day. A well-run email‑based process can still be fair; a platform just makes fairness the default and the audit trail automatic.
Building Supplier Relationships: Checks That Build Trust, Not Friction
Vetting does not need to feel adversarial. You can set a high bar while signalling partnership. The secret is relevance, proportionality and clarity.
- Ask only what you need. Keep questionnaires lean and aligned to risk. If a micro‑supplier provides a low‑risk service, do not bury them in enterprise‑grade paperwork.
- Explain the why. A short note on why you ask for insurance levels or incident histories reduces defensiveness and improves quality of responses.
- Offer examples and templates. Provide sample answers or redacted policies to show the level of detail expected. This avoids guesswork and repetitive questions.
- Be open on timelines. Publish your evaluation schedule and stick to it. Suppliers appreciate predictability, and your team benefits from fewer chase‑ups.
- Close the loop. Share feedback post‑award. It improves the market and pays back on your next competition with stronger bids.
Trust compounds. When suppliers see that your process is fair, sealed, and anchored in evidence, more of the right vendors will show up with their best work. That is good for competition and great for outcomes.
Frequently Asked Questions
How often should we update our supplier vetting criteria?
Review quarterly and after any significant policy or regulatory change. In practice, most teams tune weights and wording every few tenders as lessons emerge. Run a quick Red Team review before each new competition, and a deeper refresh annually to align with company risk appetite and the market you buy from in 2026.
What’s a sensible minimum for financial checks on small contracts?
Confirm company identity and active status, look for overdue filings, and review key ratios or credit indicators proportionate to spend and criticality. For micro‑contracts, a light check often suffices; for critical services, assess liquidity and continuity plans. Document your threshold logic so auditors can see why you sized the check that way.
Do we need ISO certifications to pass vetting?
No. Certifications can signal maturity but are not a guarantee of fit. Focus on demonstrable controls and processes relevant to your scope—incident response, access management, quality control and change management. If you require specific standards, state them early and allow equivalent evidence so capable suppliers are not unfairly excluded.
How can we reduce bias when evaluating qualitative answers?
Use anchored scoring rubrics, blind technical reviews, and independent moderation. Train reviewers on common cognitive biases and keep supplier names and logos out of the initial pass. Require evidence citations in comments so scores tie to text, not perception. Tools that enforce side‑by‑side comparisons also help.
What should feedback to unsuccessful suppliers include?
Reference published criteria, share relative strengths and weaknesses with examples, and avoid revealing others’ confidential details. Offer a short call if feasible. Clear feedback improves supplier capability and signals that your process is worth investing in next time, strengthening your future competitions.
Ready to modernise your vetting and run sealed, evidence‑led awards? Visit TenderLock to see how fast you can go from brief to defensible decision—your first live tender is free.