A supplier vetting checklist is a structured list of criteria and evidence you gather to confirm a supplier’s capability, compliance and risk posture before you award a contract. It keeps decisions consistent, auditable and fair, so your team can compare like‑for‑like responses and demonstrate clear governance if challenged later.
What Is Supplier Vetting and Why It Matters in 2026?
Put simply, supplier vetting is the process of confirming that a prospective supplier can do what they claim—safely, legally and reliably—before you commit spend. In 2026, public expectations and board‑level scrutiny have never been higher. Whether you’re a scale‑up outsourcing your first managed service, or an enterprise consolidating a complex supply base, strong vetting protects against service failures, reputational harm and regulatory breaches.
Good vetting feels boring in the best way. It’s predictable, repeatable and lightly automated, so you can invest your human time in interpretation rather than admin. At its heart are three pillars: capability (can they deliver?), compliance (are they allowed to?), and risk (what could go wrong and how will we know?). A clear supplier vetting checklist ensures you capture the right evidence for each pillar—without drifting into paperwork theatre.
The trick is balance. You want checks that scale with risk: a simple low‑value software tool needs less scrutiny than a critical data processor or a construction contractor. This is where structured requirements, weighted criteria and a standardised audit trail come in. Tools like TenderLock formalise those expectations from the brief onward, so your team can be consistently thorough without reinventing the wheel for every purchase.
The Essential Supplier Vetting Checklist
Here’s how seasoned procurement teams break the task down. The aim is to translate your buying brief into verifiable criteria, and then ask for evidence tied to each criterion. Your supplier vetting checklist becomes both the instruction to bidders and the yardstick for evaluation—no surprises, just clarity.
| Criterion | Why It Matters | Acceptable Evidence | Helpful Automation |
|---|---|---|---|
| Legal identity and status | Confirms the entity you’ll contract with exists and is in good standing. | Registered name, company number, incorporation docs. | Automated lookup via Companies House; alerts for name/number mismatch. |
| Financial health | Assesses ability to fulfil the contract over time. | Filed accounts, liquidity indicators, credit scores, parent guarantees. | Integrated credit checks (e.g., Creditsafe), threshold‐based flags. |
| Technical capability | Proves they can deliver the scope at the required quality. | Case studies, references, CVs of key staff, certifications. | Requirement‐by‐requirement evidence prompts and validation. |
| Information security | Protects data and business continuity. | ISO/IEC 27001, SOC 2, policies, penetration test summaries. | Policy templating, evidence locks, risk register linkage. |
| Compliance and ethics | Addresses statutory duties and modern expectations. | Anti‐bribery, Modern Slavery, equality, ESG statements. | Red Team ambiguity checks; clause‐by‐clause attestations. |
| Health and safety | Critical for on‐site or physical works risk. | Policies, RIDDOR history, method statements, RAMS. | Template RAMS prompts; incident history capture. |
| Insurance cover | Ensures adequate protection if something goes wrong. | Employer’s, public/professional liability certificates; limits and expiry. | Expiry date tracking and automated reminder workflows. |
| Delivery approach and SLAs | Sets expectations and measures of success. | Project plan, milestones, service levels, escalation paths. | Weighted criteria with outcome‐based scoring guides. |
| Pricing structure | Supports apples‐to‐apples comparison and whole‐life value. | Itemised pricing, rate cards, indexation, assumptions. | Normalised pricing forms; sealed bids until deadline. |
| References and track record | Third‐party confirmation of performance. | Contactable referees, KPIs delivered, lessons learned. | Recorded calls with AI summaries; evidence‐locked notes. |
With TenderLock, you can convert a plain‑English buying brief into structured requirements, automatically attach evidence fields, and run checks end‑to‑end. This reduces back‑and‑forth and keeps your supplier vetting checklist tightly aligned with what you’re actually buying.
For deeper context on the UK regulatory lens and practical templates, see our ultimate guide to UK supplier checks. It complements this FAQ by zooming into risk tiers, document examples and renewal cycles.
How Do You Assess Financial Stability Without Overcomplicating It?
Financial checks should be proportionate, explainable and repeatable. Start with identity: confirm the legal entity’s registered name and number, and that it’s active. Next, review recent filings. For UK entities, Companies House provides directors, charges and accounts, which you can triangulate with a credit report. If the bidder is part of a group, consider whether a parent guarantee is appropriate for your risk appetite.
For SMEs or early‑stage suppliers with thin filings, lean more on forward‑looking indicators: liquidity buffers, pipeline concentration, and scenario plans if a key customer churns. Ask for bank letters only where genuinely necessary; many robust indicators are in public filings or can be requested as redacted extracts. In your supplier vetting checklist, keep thresholds clear (e.g., minimum current ratio) and allow context statements where outliers appear.
TenderLock integrates Companies House checks and Creditsafe scoring so you can set alert thresholds and document exceptions. If a supplier triggers a flag—say a director change plus a thin cash position—you can escalate for a commercial guarantee or phased payment schedule. Crucially, note decisions in the audit trail with named approvers, so your rationale is recoverable during audits or disputes.
Can AI Improve Fairness and Consistency in Vetting?
Yes—when used to structure information, not to replace judgement. AI helps translate human briefs into precise, testable requirements, and can spot ambiguity before suppliers see the documents. TenderLock’s Red Team reviews flag vague terms, missing acceptance criteria and contradictions, so bidders aren’t second‑guessing what “robust”, “secure” or “fast” means. That alone improves fairness.
During evaluation, requirement‑by‑requirement checks ensure assessors score like‑for‑like evidence, with guidance notes and examples visible inline. Responses and attachments are evidence‑locked, preserving the record exactly as submitted. Named human evaluators still make decisions; the platform simply reduces subjectivity creep. If you’re standardising on a supplier vetting checklist across teams or regions, this consistency is golden.
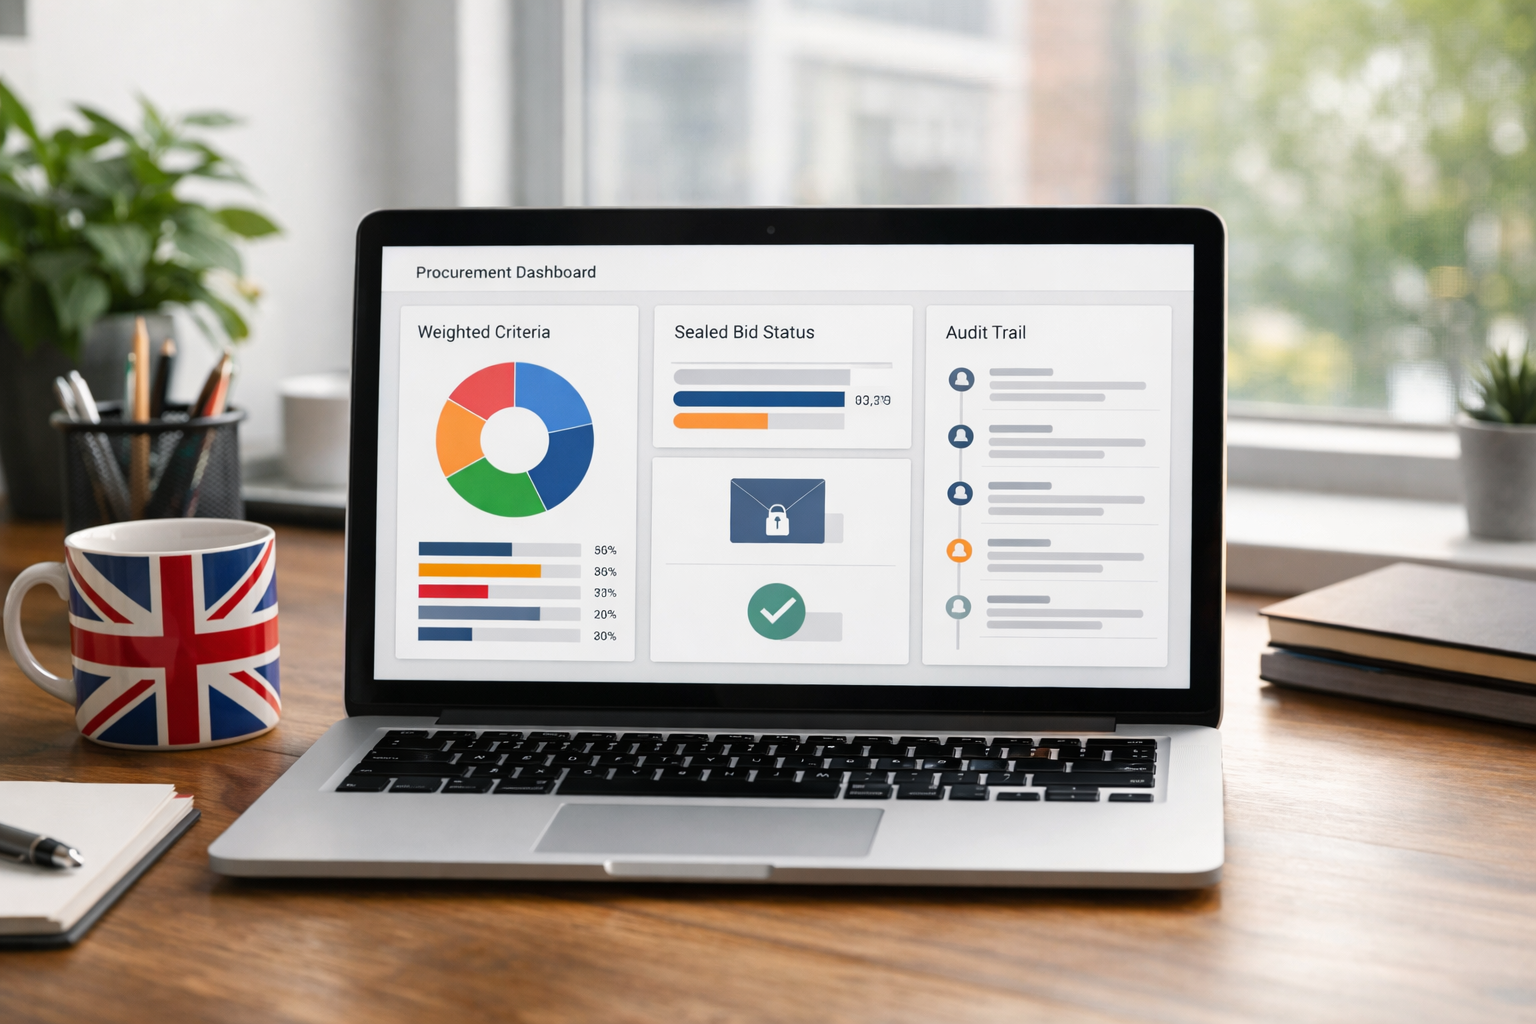
Sealed bids remain sealed until the deadline, protecting commercial integrity. After opening, dashboards show progress by criterion, not just by supplier, exposing gaps early without revealing pricing prematurely. If you’re ready to see this in action on a real opportunity, start a free live tender with TenderLock—no card required, full audit trail included.
How Do You Run Sealed, Auditable Evaluations?
Think of a sealed, auditable evaluation as three phases: set‑up, controlled exchange and decision. In set‑up, translate your scope into structured requirements and weights. Publish a timetable, clarify rules for Q&A, and define who can see what. During the controlled exchange, suppliers submit into sealed envelopes; your team issues any clarifications to all bidders equally. Only at deadline are bids opened, and even then, visibility is role‑based.
From there, assign criteria to named evaluators. Work requirement‑by‑requirement rather than supplier‑by‑supplier to avoid halo effects. Capture reasons for scores immediately and lock them with the evidence they reference. If you invite presentations or site visits, record them and attach AI summaries into the same criterion record. Finally, hold a moderation meeting with a clear agenda: reconcile outlier scores, ensure weightings were applied, and confirm that any risk mitigations are funded or contractually assured.
For a practical walkthrough, including how to structure scoresheets and moderation notes, read our AI‑assisted sealed bidding walkthrough. It pairs well with a living supplier vetting checklist to keep your governance clean under time pressure.
What Checks Are Non‑Negotiable for UK Compliance?
Legal frameworks evolve, but several anchors remain steady in 2026. Data protection duties are set out by the UK GDPR and the Data Protection Act 2018; when processing personal data, ensure contracts include controller‑processor roles, sub‑processor controls, and incident response. The ICO guidance on data protection is the canonical reference for clauses and accountability.
For labour standards, verify Modern Slavery statements (where thresholds apply) and ensure your supplier’s due diligence runs deeper than a policy on paper. For physical works or on‑site services, the HSE guidance on managing contractors outlines responsibilities for competence checks, RAMS, and supervision. Embed these expectations in your contract schedules, not just your tender questions, and keep renewal dates visible.
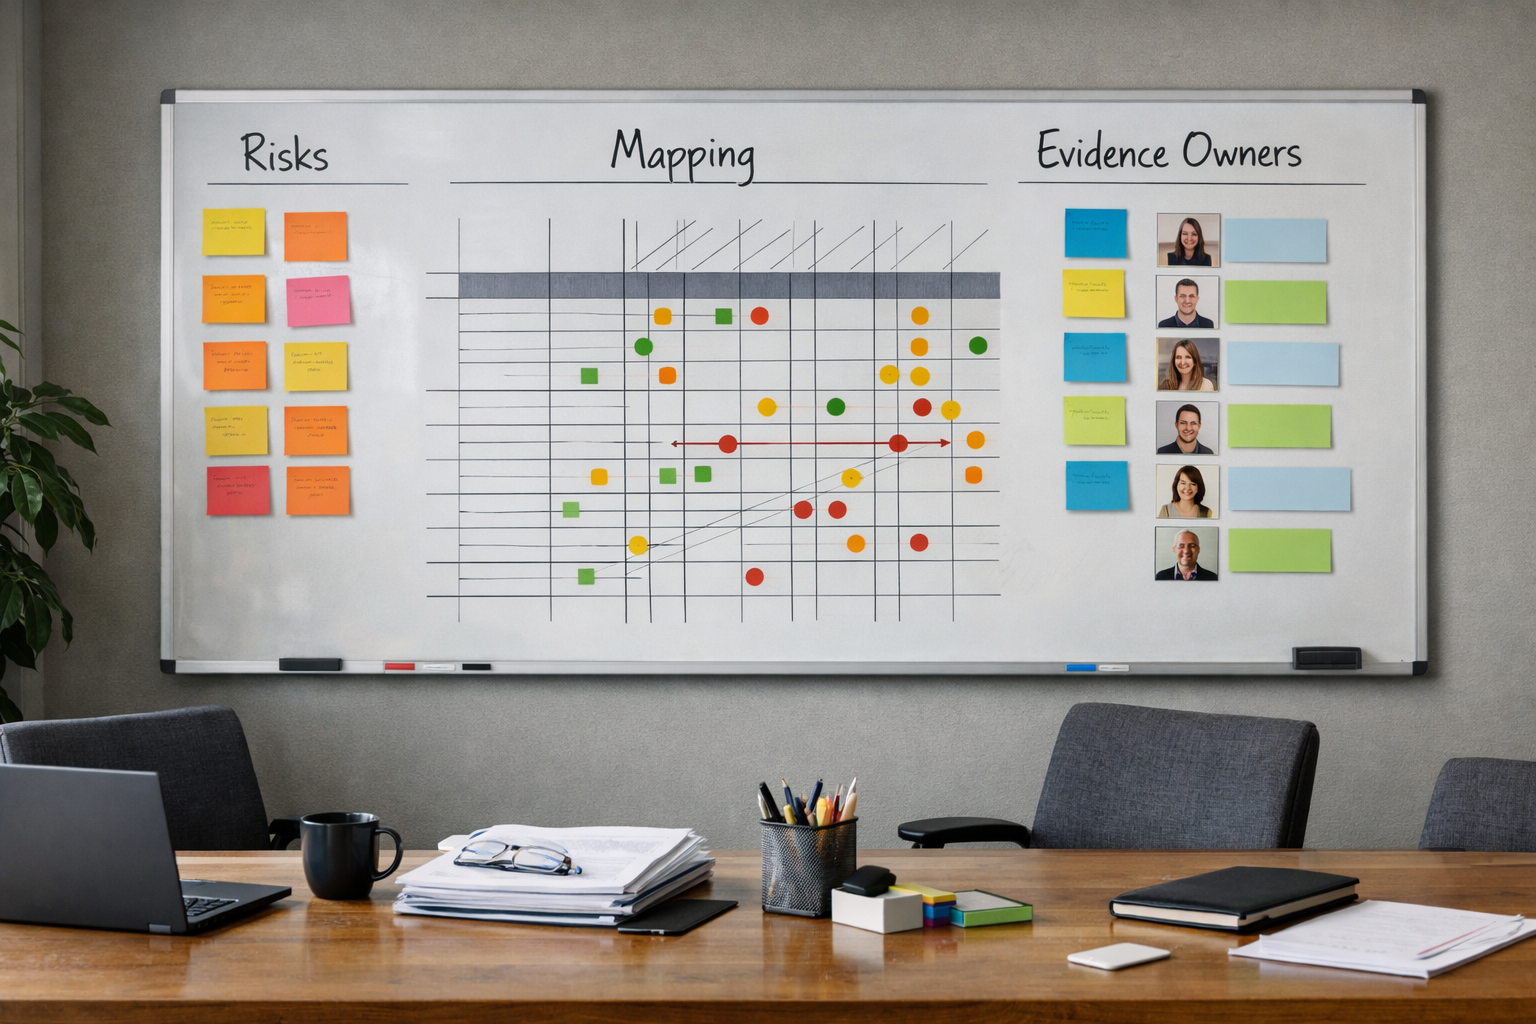
A practical move is to maintain a compliance annex in your supplier vetting checklist that maps specific evidence to named risks: for example, ISO/IEC 27001 certificate for data security; CHAS or SafeContractor accreditation for site safety; anti‑bribery training logs for ethics. Tie each item to an owner and review cycle, so that renewals and audits don’t rely on inbox archaeology.
Scoring Methods and Weighting: Getting Them Right
Weighting is your tool for signalling what matters. Start by translating outcomes into criteria, then allocate weight by business value and risk. A typical pattern: 35–45% quality (solution fit), 25–35% commercial (total cost of ownership), 10–20% service (SLAs and support), 10–20% compliance and risk. For simple buys, reduce criteria; for critical, expand and split sub‑criteria.
Scoring models vary. A 0–5 scale with defined descriptors keeps calibration sane; narrative‑only scoring often drifts. Consider price normalisation to prevent distorted results (e.g., lowest compliant bid gets max price points; others receive proportionate scores). Whatever model you adopt, publish it upfront—suppliers can align responses better, and evaluators can defend their decisions.
| Approach | When to Use | Pros | Watch‐outs |
|---|---|---|---|
| 0–5 calibrated scale | Most tenders with mixed qualitative and quantitative criteria. | Comparable, trainable; supports moderation. | Needs strong descriptors to avoid mid‐score clustering. |
| Pass/Fail gateways | Mandatory compliance items (e.g., insurance, certifications). | Fast elimination of non‐compliant bids. | Overuse can exclude innovative options prematurely. |
| Weighted price normalisation | Price‐sensitive but quality‐dependent buys. | Prevents extreme price outliers dominating. | Check math transparency; explain the formula to bidders. |
Lock your scoring guidance next to each criterion. In TenderLock, that includes examples of what a 2 vs a 4 looks like. If your supplier vetting checklist calls for reference calls or demos, add mini‑rubrics there too, so presentations don’t become free‑form showpieces that skew results after the fact.
Communicating With Suppliers: Questions, Clarifications and Debriefs
Supplier communication should create clarity without leaking advantage. Keep Q&A centralised and share any material clarification with all bidders. Be specific with deadlines and formats for responses. If a question reveals ambiguity in your documents, fix the documents—don’t patch via email threads that later vanish from your record.
When you run interviews, site visits or demos, record sessions and attach AI‑generated summaries to the relevant criteria. This keeps performance claims, commitments and dependencies tied to the evidence you’ll score. It also speeds up debriefs. After award, provide constructive feedback grounded in your criteria and weighting, not generalities. This builds market trust and improves future bids.
In practice, a strong supplier vetting checklist includes communication checkpoints: Q&A windows, clarification cut‑offs, and planned debrief outlines. TenderLock bakes these into timelines and binds notes to the evaluation record, protecting you if decisions are questioned months later.
Common Pitfalls and How to Avoid Them
Even experienced teams can stumble into avoidable traps. Here are patterns to watch for, plus ways to counter them gracefully without slowing everything down.
- Vague requirements: Words like “robust” or “industry‑leading” create scoring fog. Counter with acceptance criteria and measurable service levels. TenderLock’s Red Team review flags ambiguity before release.
- Over‑collecting paperwork: More documents aren’t more assurance. Anchor each request to a criterion in your supplier vetting checklist, and drop anything that doesn’t change a decision.
- Halo and recency bias: Evaluating one supplier end‑to‑end can colour judgement on the next. Score requirement‑by‑requirement, with named evaluators and locked rationales.
- Price myopia: A headline discount can hide whole‑life costs. Normalise price, validate assumptions, and model indexation or exit costs.
- Weak audit trail: Decisions made in chat threads are invisible at audit. Keep all evidence, notes and approvals in one place, with timestamps and roles.
- Unmanaged renewals: Insurance and certifications expire mid‑contract. Track expiries with alerts; escalate lapses automatically.
Finally, don’t skip reference validation because time is tight. Short, structured calls—recorded and summarised—often surface delivery behaviours you won’t see in glossy case studies. Build them into your timetable, not as optional extras but as scored evidence points.
Frequently Asked Questions
What documents should you request from a new supplier?
Start with legal identity (name, number), insurance certificates, and relevant certifications (e.g., ISO/IEC 27001 for security). Add two recent case studies with contactable referees, financial filings or a recent credit report, and policies for data protection and ethics. Map each document to a criterion so your requests stay lean and purposeful.
How often should you re‑vet existing suppliers?
Set cycles by risk. For critical or high‑risk suppliers, annually is typical; for lower‑risk, every 24–36 months can work. Time‑bound items (insurance, certificates) should trigger alerts ahead of expiry. If scope changes materially—or incidents occur—bring forward a review. Make the cadence part of your contract schedules in 2026 to avoid drift.
Should SMEs be held to the same standards as large enterprises?
Standards should match risk, not company size. Apply the same principles, but allow proportionate evidence. For example, a start‑up might show audited policies and secure architecture diagrams rather than a full certification. Your supplier vetting checklist should offer compliant alternatives, so innovation isn’t excluded by paperwork alone.
How do you handle conflicting references or mixed feedback?
Probe for specifics: what, when, and how issues were resolved. Weigh patterns over isolated anecdotes and compare against your criteria. If concerns remain, consider a pilot, phased ramp‑up, or commercial protections (e.g., retention). Record the rationale and any mitigations in the audit trail, so governance is clear if challenged.
Is it acceptable to accept self‑certifications?
Sometimes, yes—if risk is low and you plan to verify post‑award. For higher‑risk areas (security, safety, regulated processes), prefer third‑party certificates or attested evidence. If you use self‑certs, state the conditions, verification timelines, and consequences in your documents, and track them like any other commitment.
Ready to raise the bar? Start your first live tender free with TenderLock and standardise your vetting process without adding busywork. Your team keeps control; the platform handles the structure, sealing and audit trail.