A Tender Evaluation Criteria Example: An AI-Assisted Scenario Walkthrough
3 November 2026 · 13 min read
Here is a tender evaluation criteria example in plain English: list what matters, weight it, define what good looks like, and score consistently against evidence. Below we walk through a realistic, hypothetical scenario end to end, showing how to turn a buyer’s brief into structured criteria, run a sealed process, and award transparently with a defensible audit trail.
What Are We Evaluating, and Why Does It Matter?
When you buy through a formal tender, you are not just comparing prices. You are testing a supplier’s capability to deliver outcomes, reduce risk and add value over time. That means your criteria need to convert a narrative brief into measurable requirements, with clarity about minimum pass/fail thresholds, weighted quality factors and a pricing model you can compare fairly. The result is a scoring framework where each point has meaning—not guesswork.
Strong criteria achieve three things. First, they translate organisational needs into verifiable deliverables, so evaluators can tick off compliance at requirement level. Second, they balance cost against quality and risk, reducing the chances of a false economy. Third, they make the decision defensible: auditors and stakeholders can see exactly why a winner was chosen, and suppliers can receive constructive, consistent feedback that maps to the published scheme.
To help, think in layers. At the base are mandatory requirements (licences, insurances, certifications, safeguards). Above those sit quality dimensions such as approach, methodology, team competence, and service levels. Overarching both is risk management—data protection, continuity, financial health—and a transparent price evaluation that considers total cost of ownership. Each element should be specific enough that two independent evaluators would score within the same band for the same evidence.
The Scenario: A 40‑Person Firm Buying Managed IT Support
Imagine a 40-person professional services firm with offices in two UK cities. Its servers have largely moved to a reputable cloud platform, but there are on‑premise devices to manage, laptops to secure and a need for 24/7 incident response. The firm has had sporadic downtime and wants to formalise support with a three‑year, renewable managed service agreement. Budget is meaningful, but continuity, data handling and response speeds are critical.
In this tender evaluation criteria example, the buyer issues a brief explaining business context, target service outcomes (uptime, SLAs, first-time fix), security expectations (MFA, endpoint protection, patch cadence), onboarding timeline and a rough device count. They plan a sealed bid to avoid anchoring or informal price signalling. A cross‑functional evaluation team will score quality independently before price is revealed, and final award will require named approvals.
The buyer invites four pre‑qualified suppliers to respond. Each is asked to provide: (1) a compliance statement to mandatory requirements, (2) a method statement covering service transition and BAU operations, (3) team biographies and roles, (4) a risk register with mitigations, (5) a pricing workbook with unit rates and scenarios, and (6) references and sample reports. Clarification questions are allowed during the window, all answers shared with every bidder.
Tender Evaluation Team, Roles and Decision Gates
Good governance starts with defined roles. For our hypothetical buyer, there is a Procurement Lead (process owner and conflict-of-interest checks), a Technical Lead (service and security depth), an Operations Manager (user impact and SLA practicality), and a Finance Partner (price methodology and affordability). Each evaluator scores independently against the published scheme, then a moderation session records rationales and resolves material variance.
Decision gates reduce bias. Gate 1 is a pass/fail screen for mandatory requirements: insurances, accreditations, data protection controls, and the ability to mobilise within the onboarding window. Gate 2 is the quality scoring on method, service and team. Gate 3 is the commercial evaluation, which applies a transparent formula to submitted pricing. The final gate is executive sign‑off, confirming the process followed the rules and that risks are understood and accepted.
Two governance practices help here. First, maintain an auditable trail of who read what, scored what, and when, with evidence linked to specific requirements rather than general impressions. Second, record any supplier interactions—clarification calls, demos—and summarise them factually so all evaluators are working from the same information. For public sector buyers, see the high‑level principles in public sector procurement policy on transparency and equal treatment, which also inspire good private-sector discipline.
A Tender Evaluation Criteria Example You Can Reuse
Below is a structured, hypothetical criteria set for managed IT support. It is designed to be simple to understand, easy to score, and adaptable for scale. This tender evaluation criteria example assumes quality and risk together carry more weight than pure price, but the weights can be tuned to your context. It also uses requirement‑level checks for pass/fail items before you score anything else.
| Criterion | Weight | How It Will Be Scored | Evidence Expected |
|---|---|---|---|
| Mandatory Compliance (Pass/Fail) | 0% | All mandatory items must pass, else bid is non‐compliant. | Insurance certificates, key accreditations, data protection policy, service coverage statement. |
| Service Transition & Onboarding | 20% | 0–5 scale for clarity, realism, risk handling, and timeline. | Transition plan, RACI, asset discovery approach, cutover plan, early life support. |
| Operations & Incident Management | 20% | 0–5 for SLAs, response/resolve targets, escalation paths, tooling, reporting. | SLAs, sample dashboards, sample weekly/monthly reports, on‐call rota. |
| Security & Compliance | 20% | 0–5 for endpoint standards, patch cadence, vulnerability handling, data handling. | Security standards, MFA/EDR approach, patch/change process, incident response outline. |
| Team & Experience | 10% | 0–5 for relevant certifications, similar‐size clients, stability, named leads. | CVs/biographies, org chart, certifications, case outlines (no client names required). |
| Risk & Continuity | 10% | 0–5 for identified risks, mitigations, continuity plan, backups, DR testing. | Risk register, BCP summary, backup policy, RTO/RPO commitments. |
| Price & Commercials | 20% | Normalised formula on total cost of ownership; clarity on assumptions. | Pricing workbook (unit rates and bundles), scenario pricing, indexation terms. |
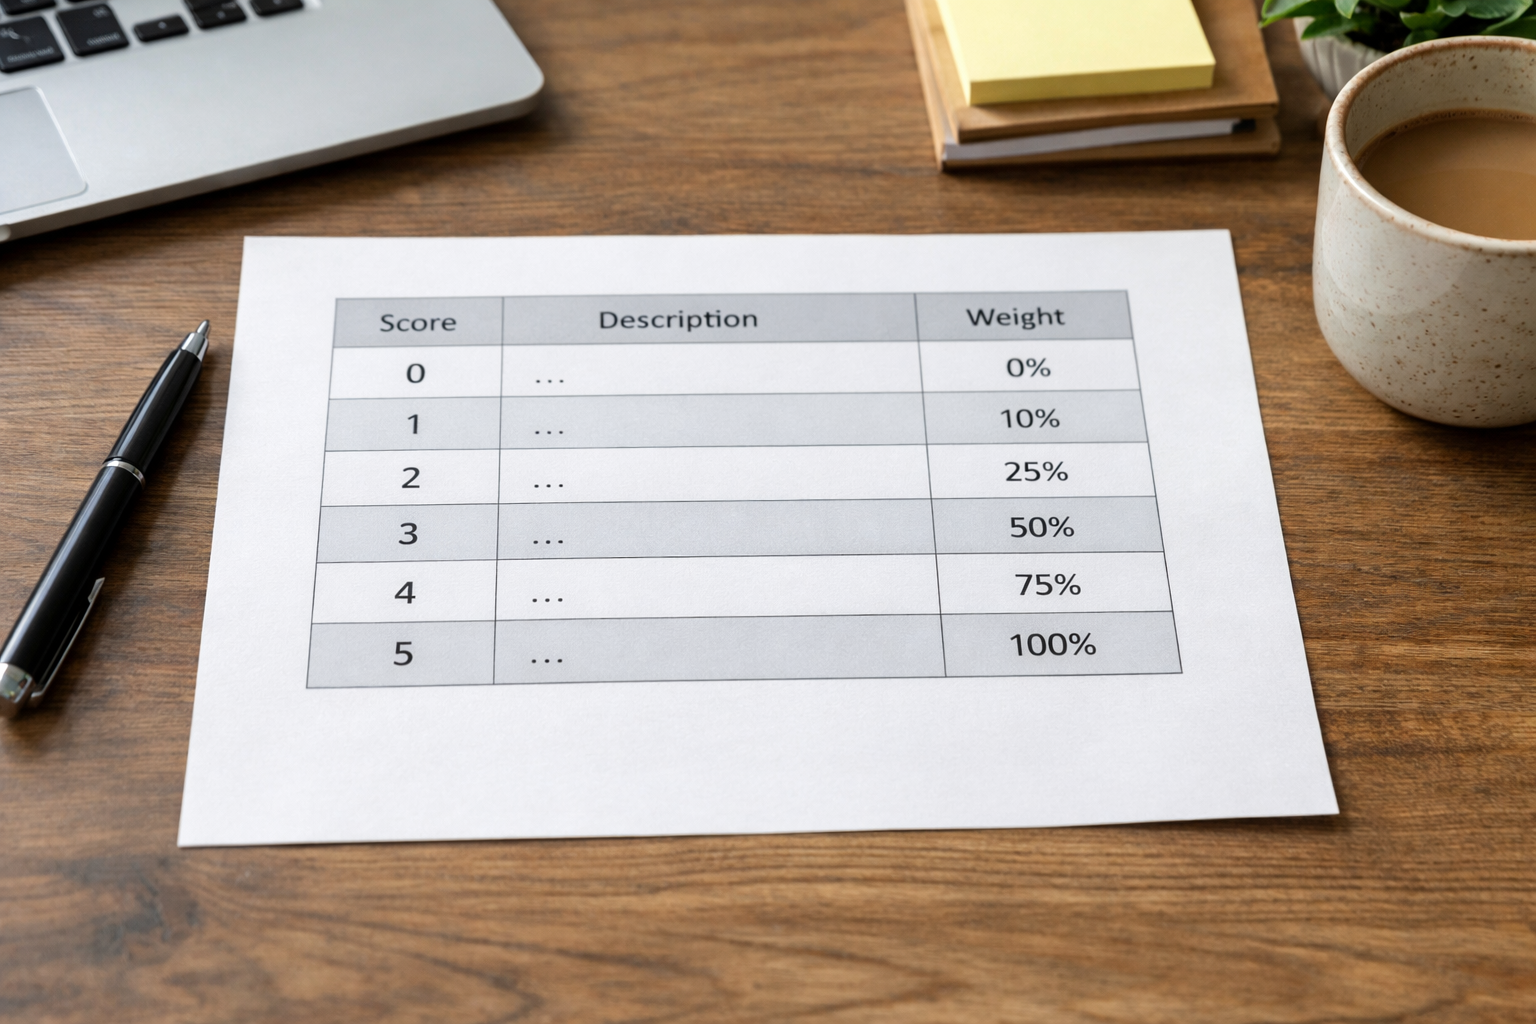
Scoring guidance should accompany the scheme. For a 0–5 scale: 0 = no answer or non‑compliant; 1 = limited, major gaps; 2 = adequate but risk remains; 3 = good and credible; 4 = strong, low residual risk; 5 = excellent, fully evidenced and tailored. Publish that guidance to suppliers upfront so expectations are aligned, and evaluators have a common language.
How Do You Weight Quality vs Price vs Risk?
There is no universal ratio, but the weightings must reflect how failure would impact your organisation. A law firm handling sensitive client data may push Security & Compliance higher than a creative agency buying print services. A start‑up seeking runway extension might weight price more heavily while still imposing non‑negotiable pass/fail controls. When adapting any tender evaluation criteria example, align it to business risk tolerance and value drivers.
A practical method is to start with your risk register and service goals. Ask: if the supplier under‑delivers this element, what happens? Quantify impact (financial, operational, reputational) and likelihood. The higher the product of impact and likelihood, the higher the weight should be. Then test the draft weights with stakeholders not on the evaluation panel, to surface blind spots. Small rebalancing now can prevent regret later.
Price evaluation deserves its own design. Normalise costs to a base scenario (e.g., 40 users, 50 devices, standard hours, typical incident volume). Require unit rates for common add‑ons so growth doesn’t spiral. Then choose a transparent formula that rewards best value, not just lowest sticker price. As one example, award 100% of the price score to the lowest total and reduce others proportionally, while still disqualifying abnormally low bids if the overall proposal is unsustainable.
What Does Good Evidence Look Like?
Evaluators need evidence, not promises. For transition, look for a timeline with clear handoffs and early life support. For operations, ask for sample dashboards and report templates that show how SLAs are tracked. For security, expect a policy summary with concrete controls: MFA enforced, patch windows, EDR tooling and response pathways. For team competence, named people with relevant certifications and actual role coverage during business and out‑of‑hours periods.
Vetting supports the picture. Check legal details through Companies House service and review financial indicators through an appropriate bureau. Validate data protection posture against UK GDPR principles outlined by the Information Commissioner's Office. Where suppliers cite standards like ISO 27001, ask for certificate numbers and scope statements, not just a logo in a slide deck.
As you collect evidence, keep it attached to the requirement it proves. That way, moderation discussions aren’t anecdotal, and your audit trail is simpler. If you’re new to vetting structures and what to request, the Supplier Vetting Checklist UK guide offers an extensive, practical run‑through tailored to 2026 buyers and SMEs stepping into more formal procurement.
Running the Sealed Bid and Clarifications
A sealed process prevents pre‑emptive price signalling and reduces anchoring bias. Practically, it means bids remain inaccessible until the deadline; clarifications are shared with all bidders; and quality scoring happens without seeing prices. You can still run demos or Q&A, but record what was shown and said, then attach those summaries to your files so each evaluator has equal context before scoring.
Plan your clarification window. Encourage questions early and publish all answers at once, anonymised. If you amend the brief, update the schedule to give reasonable time for suppliers to respond. After the deadline, lock in your evaluation timetable and stick to it. Unstructured, rolling back‑and‑forth after submission is where risk creeps in. If you need a refresher on process steps, this Sealed Bidding Process walkthrough explains the practical rhythm with AI‑assisted safeguards.
Step-by-Step Evaluation: From Lock Opening to Award
Here is how our hypothetical team proceeds after the submission deadline. First, Procurement confirms that bids are complete and opens them. Compliance checks are performed requirement‑by‑requirement: insurances, service coverage, data handling statements. Non‑compliant bids exit here, with reasons documented. Next, quality scoring begins. Each evaluator reads in full, scores independently against the scale, and writes short rationales referencing evidence items.
After independent scoring, the panel convenes for moderation. Any large variances are discussed against the published guidance: what did one person see that another did not? Rationales are refined, with supporting document references noted. Once moderated quality scores are frozen, the price evaluation is applied to the normalised scenario. The team then runs a final check that required accreditations and risk mitigations are still acceptable and lines up to the final scores.
To illustrate scoring mechanics, here is a simplified comparison across three hypothetical bidders (Quality is out of 80; Price out of 20; Total out of 100). Numbers are placeholders that demonstrate method, not outcomes:
| Bidder | Quality (80) | Price (20) | Total (100) | Notes |
|---|---|---|---|---|
| Bidder 1 | 64 | 18 | 82 | Strong security and operations; mid‐range cost. |
| Bidder 2 | 70 | 15 | 85 | Best quality; higher priced. |
| Bidder 3 | 58 | 20 | 78 | Lowest price; weaker transition detail. |
Totals alone do not tell the story; your file should show why the numbers landed where they did. The moderation note for each criterion, plus references to evidence, makes the reasoning explicit and reproducible. Where commercial differences are tight, it’s common to run a brief verification session to confirm understanding, but avoid introducing new content not present in the written bid, to keep a level field.
Common Pitfalls and How to Avoid Them
Ambiguity in criteria is a frequent cause of weak competition. If two reasonable suppliers could misread your requirement in different ways, you’ll receive apples‑to‑oranges proposals and an unhappy scoring session. Red team your own brief: have someone uninvolved try to respond to it; wherever they had to guess, add precision. A common trap in a tender evaluation criteria example is a broad “innovation” criterion with no definition of value or evidence—avoid that.
Another risk is price myopia. The cheapest bid sometimes looks appealing, but total cost of ownership includes service credits that never compensate for lost productivity, or change costs you didn’t model. Conversely, over‑weighting a pet quality area can bias the outcome without improving delivery. Balance comes from candidly assessing risk and ensuring your weights signal what truly matters to the business, then sticking to the plan you published.
Finally, shortcuts during moderation can erode fairness. If rationales aren’t tied to specific evidence, you will struggle to explain the decision to stakeholders or to the market. Keep minutes, capture dissent briefly, and confirm conflict‑of‑interest declarations are up to date. For regulated entities, parity of information and auditability are not optional; for private buyers, they are the foundation of supplier trust and market reputation.
How TenderLock Streamlines Criteria, Scoring and Audit
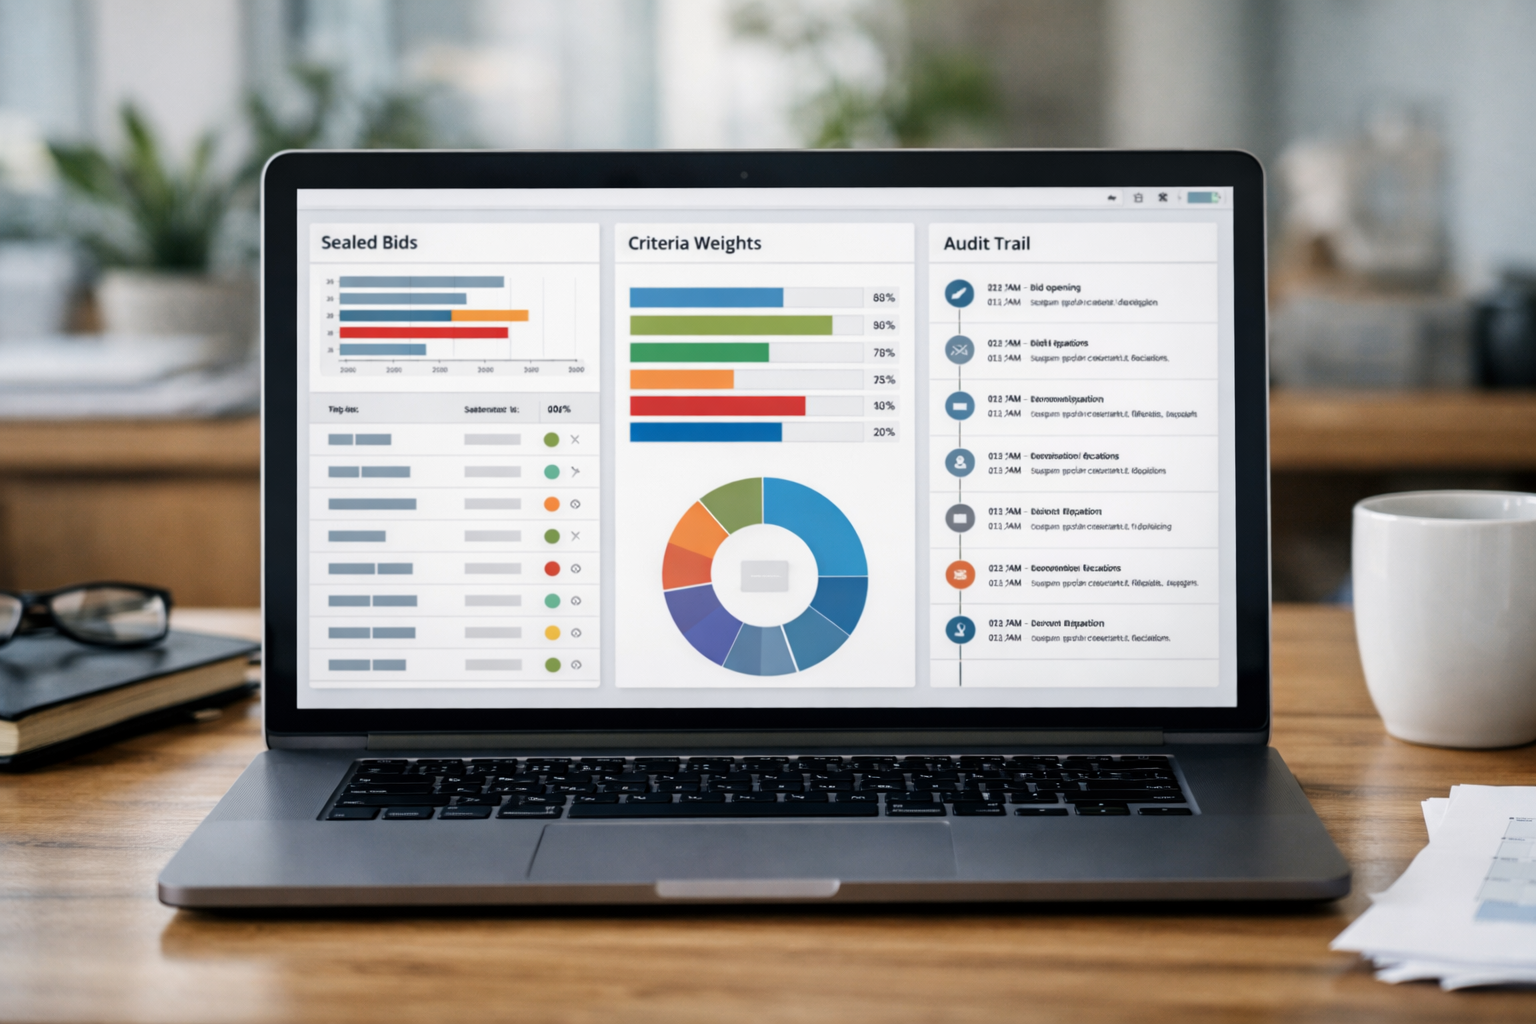
Platforms can remove admin friction and harden governance. TenderLock converts your plain‑English brief into structured requirements with weighted criteria, then keeps bids locked until the deadline. During evaluation, requirement‑by‑requirement checks, evidence‑linked scoring and named approvals ensure the people you nominate make the final call. Recorded supplier calls receive AI summaries so every evaluator works from the same facts, and a full audit trail is built automatically.
The product also supports red team reviews to catch ambiguity, Companies House lookups and third‑party risk indicators, plus dashboards that show scoring dispersion before and after moderation. Because the logic is transparent, you can re‑use and refine schemes across future buys. TenderLock turns a tender evaluation criteria example into repeatable templates that scale from SME teams to enterprise groups—all while maintaining sealed, fair bidding.
If you’re ready to try this workflow without procurement overhead, you can start your first tender free. No card needed, and your live tender runs under proper locks, with evidence‑based scoring and auditable approvals from brief to award.
Frequently Asked Questions
How many criteria should a small business include?
Keep it focused. Five to eight weighted quality dimensions, plus pass/fail checks, is plenty for most SME tenders. Too many criteria create overlap, evaluator fatigue and noisy results. Group related points (e.g., incident management and reporting) and use scoring guidance so evaluators apply the same yardstick. If in doubt, combine or drop low‑impact items and keep your audit trail tight.
What scoring scale works best in 2026?
A 0–5 scale balances nuance with usability. It’s granular enough to separate bids and simple enough for consistent application. Publish descriptors for each band, from “no evidence” to “excellent, fully evidenced and tailored.” Calibrate with one or two practice scores before going live, then lock the scheme. Consistency in application matters more than the exact number of points.
How do we compare prices fairly without overcomplicating it?
Normalise to a base case: define users, devices, hours and typical incident volume. Require unit rates for common changes. Score with a transparent formula that awards maximum points to the lowest comparable total and scales others proportionally. Flag abnormally low bids for viability checks rather than rewarding unmanageable pricing that risks service failure later.
Can we ask for demos without biasing the process?
Yes, with rules. Schedule equal time per supplier, share the same agenda and scenarios, and record sessions. Provide a factual summary to all evaluators and avoid accepting new content that wasn’t submitted in writing. Weight any demo‑based observations under the relevant published criteria, not as a new, off‑the‑books factor.
What evidence should we demand for security claims?
Ask for policy summaries, control descriptions (MFA, EDR, patch windows), incident response outlines, and certificate details for any claimed standards. Confirm data handling aligns to UK GDPR expectations from the ICO. For continuity, look for backup policies, tested restore times and a named owner. Evidence should be specific, current and scoped to your environment, not marketing copy.
Run Your First Sealed Tender Free
If you’ve read this far, you likely have a live need that deserves a clear, fair and fully auditable process. With TenderLock, you start from your plain‑English brief and end with a defensible award, all in one place. The platform converts your words into structured requirements and weights, seals bids until the deadline, and guides your team through requirement‑level checks, independent scoring and named approvals with a built‑in audit trail.
You also get pragmatic extras that matter in the real world: red team reviews to catch ambiguity before it hits the market, integrated company checks, evidence‑locked rationales, and recorded supplier calls with AI summaries so everyone evaluates the same facts. Whether you’re a 10‑person start‑up or an enterprise team seeking consistency across categories, you’ll save hours and gain confidence in the outcome.
Want to see it in action? Explore our beginner‑to‑expert tender checklist for more structure, or jump in and start your first tender free today. In a few minutes, you’ll have a published plan, sealed submissions, and the governance your stakeholders expect.